Nonprofit/ Exempt Organizations
What Is Worrying Our Nonprofit Clients – Part IV: When Cybersecurity Risks Become Mission Risks
September 28, 2026
As part four of our series on what keeps our nonprofit clients up at night, we turn to security and operational risk. For nonprofits operating with limited resources, stretched staff, and lean administrative teams, a cyber incident can quickly become much more than an IT problem. A serious data or cyber breach can interrupt services, expose sensitive information, drain financial resources, damage donor confidence, and consume management attention at the worst possible time. Beyond that, data privacy and cyber security implicate areas of serious statutory, regulatory, and potentially liability risk. Nonprofits need to acknowledge that cybersecurity is now a core governance, financial, and mission critical issue.
Cybersecurity As a Governance Issue
Nonprofit board members do not need to become cybersecurity experts. Boards do need to make sure management identifies the organization’s critical systems and sensitive information, identifies major vulnerabilities, procures appropriate resources and insurance, and develops appropriate response plans before an incident erupts.
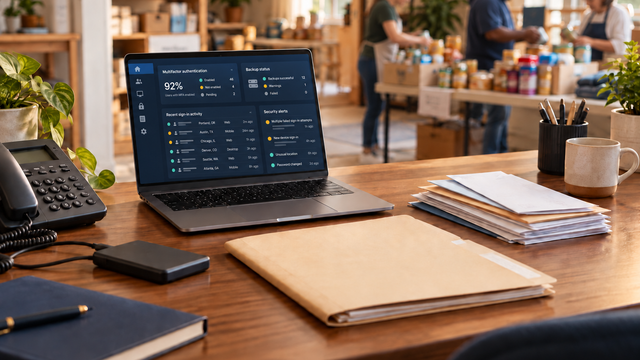
The NIST Cybersecurity Framework 2.0 provides clear guidance. Oversight must happen before a crisis. Boards should ensure the organization identifies sensitive information and establishes appropriate storage and access. Organizations need to vet their vendors to support critical operations, whether basic protections such as multifactor authentication and tested backups are in place, and whether the organization’s cyber insurance matches its actual risks. Vendor access should be limited to those that truly need access.
Boards should ensure proper risk management and response plans are developed. Who will make decisions when something goes wrong? When should counsel or the insurer be contacted? Who communicates with employees, donors, clients, patients, or regulators? Who has authority to shut down a compromised system? Those questions are much easier to answer in a boardroom than in the middle of the crisis of a ransomware attack.
Who is “The Weakest Link”?
Most cyber events rely on social engineering as opposed to pure hacking. A criminal impersonates an executive director, board chair, employee, or trusted vendor. An email changes payment instructions. A text says the request is urgent. These methods only become more effective when you layer AI-generated voicing that sounds exactly like someone the employee knows.
The best defense is to establish immutable simple controls that cannot be bypassed by a false sense of urgency. No single employee should be able to create a vendor, change banking information, approve an invoice, and release payment. Significant checks, wires, and electronic transfers should require meaningful secondary approval. Changes to banking instructions should be independently verified using trusted contact information already on file. People need to pick up the phone and call to verify information and changes as opposed to relying on email notices.
Boards also should understand who performs bank reconciliations, checking signing authority, whether that person is independent of the payment process, and whether available bank alerts and fraud-prevention tools are being used.
Audits Are Important, but Limited
An annual financial audit is valuable, but it is not a comprehensive fraud investigation or cybersecurity assessment. Boards should understand that distinction. Like financial audits, regular cyber and security auditing and review is best practice.
Rather than simply receiving the final audit and security reports, boards should ask what controls were reviewed, whether significant limitations existed, whether management-letter comments remain unresolved, and whether the same weaknesses or adjustments or technical suggestions appear year after year. When an audit or operational review identifies a significant problem, management should identify the fix, assign responsibility, set a deadline, and report back when the issue is closed. Reviews should produce decisions, not reports that sit unread in a shared drive. The Board can and should devote appropriate resources to address these risks.
Cyber Risk Is Operational Risk
A cyber incident does not need to involve stolen money or stolen data to become a crisis. What happens if employees lose access to email for three days? What if payroll, the donor database, the scheduling platform, or the case-management system goes down? For many nonprofits, a technology failure can quickly become a service-delivery failure.
Boards should therefore treat cyber resilience as part of ordinary business continuity. Management should know which systems must be restored first, how long the organization can operate without them, and whether workable manual alternatives exist. Backups require particular attention. Having a backup is not the same as being able to restore operations from it. Backups should be tested.
Vendor risk deserves the same scrutiny. Nonprofits routinely outsource email, cloud storage, payroll, fundraising platforms, billing, case management, and IT support. A vendor breach or outage can become the nonprofit’s operational problem immediately. Critical vendor contracts should address security requirements, incident notification, access to data, insurance, cooperation during a response, and responsibility for resulting costs.
For Health Care Nonprofits, the Stakes Are Higher
Health care and human-services nonprofits often hold medical, behavioral-health, disability, insurance, and financial information. A breach or system outage can affect not only privacy, but also scheduling, billing, access to clinical information, and delivery of patient services.
Consistent with HHS cybersecurity guidance, those organizations should pay particular attention to access controls, multifactor authentication, workforce training, termination of access for departing workers, incident planning, cybersecurity testing, and vendors that handle sensitive information or critical systems.
AI Is Both a Threat and an Opportunity
Artificial intelligence is making fraud more convincing. As the FBI has warned, voice cloning and other synthetic content can make impersonation harder to spot. Employees should not approve an unusual payment merely because an email looks authentic or a voice sounds familiar. Material or unusual requests should be confirmed through an independent channel. Even with verbal direction, employees should still stick to established control regimens.
AI also creates internal risks. Employees may expose confidential donor information, personnel matters, client records, contracts, or other sensitive information by placing it into unapproved public AI tools. Nonprofits need to take development and enforcement of AI policies seriously.
But nonprofits should not treat AI only as a threat. Used responsibly, AI can help small teams summarize information, organize data, improve workflows, prepare first drafts, and reduce repetitive administrative work. The answer is governance, not prohibition. Organizations should decide which tools employees may use, what information must stay out of those systems, when human review is required, and who evaluates the privacy, security, and contractual terms of new platforms.
Start With the Failure Points
For many nonprofits, the best first step is not buying more technology. It is identifying where the organization is most likely to fail by asking:
- Who can move money or change vendor payment information?
- Where is the organization’s most sensitive data stored, and who can access it?
- Which systems are essential to continued operations?
- Which vendors control or support those systems?
- What happens if email, payroll, or a critical database is unavailable for several days?
- If a key employee is unavailable, does anyone else know what to do?
Those questions usually reveal the priorities quickly.
Nonprofits cannot perfect cybersecurity, no one can. They do need disciplined governance, sound financial controls, realistic continuity planning, tested recovery procedures, careful vendor management, and practical rules for AI. Security and operational resilience are not distractions from the mission. They are part of what allows the mission to continue when something goes wrong.
In Part V, we will turn to another risk that nonprofits increasingly cannot ignore: political risk.
For more information or help with nonprofit strategies, governance, training, or legal compliance, please feel free to reach out to Timothy Hughes at (703) 526-5582, thughes@beankinney.com, or Doug Taylor at (703) 526-5586, rdougtaylor@beankinney.com. We work with nonprofits throughout Virginia, Maryland, and the District of Columbia.
This article is for informational purposes only and does not contain or convey legal advice. Consult an attorney. Any views or opinions expressed herein are those of the authors and are not necessarily the views of the firm or any client of the firm.